The UK's Data Protection Act 2018 can affect Jamaican firms, but a UK client, British customer or overseas supplier does not automatically bring every business activity within UK privacy law. The answer depends on the firm's UK connections, whose personal data it processes and what it does with that information. A business may also face contractual obligations imposed by a UK customer even where UK law does not directly regulate its processing.
For Jamaican organisations, the practical task is to distinguish three issues: direct application of UK legislation, obligations accepted through commercial contracts and compliance with Jamaica's own law. These can overlap, but they are not interchangeable.
Start with the activity, not the customer's nationality
A Jamaican hotel advertising specifically to people in the UK presents a different case from a local business that occasionally receives an unsolicited enquiry from London. Likewise, a Jamaican outsourcing provider handling records for a UK company is not necessarily in the same legal position as a business operating through a UK branch.
Assess each processing activity separately. Names, business email addresses, booking histories, identifiable location records and employee files can all be personal data. Corporate specifications or genuinely anonymous statistics may not be.
How the Data Protection Act 2018 fits the UK framework
For ordinary commercial processing, the UK framework combines the UK GDPR with the UK's 2018 Act. The UK GDPR supplies core rules on territorial scope, lawful processing, individual rights and organisational duties. The Act supplements those rules, including through conditions for certain sensitive information, exemptions and enforcement provisions. It also contains separate regimes for law enforcement and intelligence services.
The framework has been amended since 2018, including by the Data (Use and Access) Act 2025. Businesses should use revised legislation and check commencement provisions rather than rely on an original, unamended summary.
Jamaica's Data Protection Act, 2020 is separate legislation. Its requirements do not disappear because a business also falls within UK rules. Henlin Gibson Henlin's explanation of what Jamaica's data protection law means for businesses provides the local starting point.
Which UK connections matter?
Processing connected with a UK establishment
The first question is whether processing takes place in the context of the activities of a UK establishment. This can involve genuine activity through stable arrangements, not simply the location of a server or the place where a company was incorporated.
A Jamaican business with an operational UK office should examine how that office's activities connect to customer, employee or prospect data. The Data Protection Act 2018 has territorial provisions that must be considered alongside the UK GDPR's scope rules. A UK group company does not automatically bring every activity of every overseas affiliate within scope.
Offering goods or services to people in the UK
Under Article 3 of the UK GDPR, certain processing by a business without a UK establishment can fall within scope when it relates to offering goods or services to people in the UK. Payment is not essential.
An accessible website is not enough by itself. Relevant evidence can include UK-focused advertising, campaigns aimed at UK residents or arrangements clearly designed to serve that market.
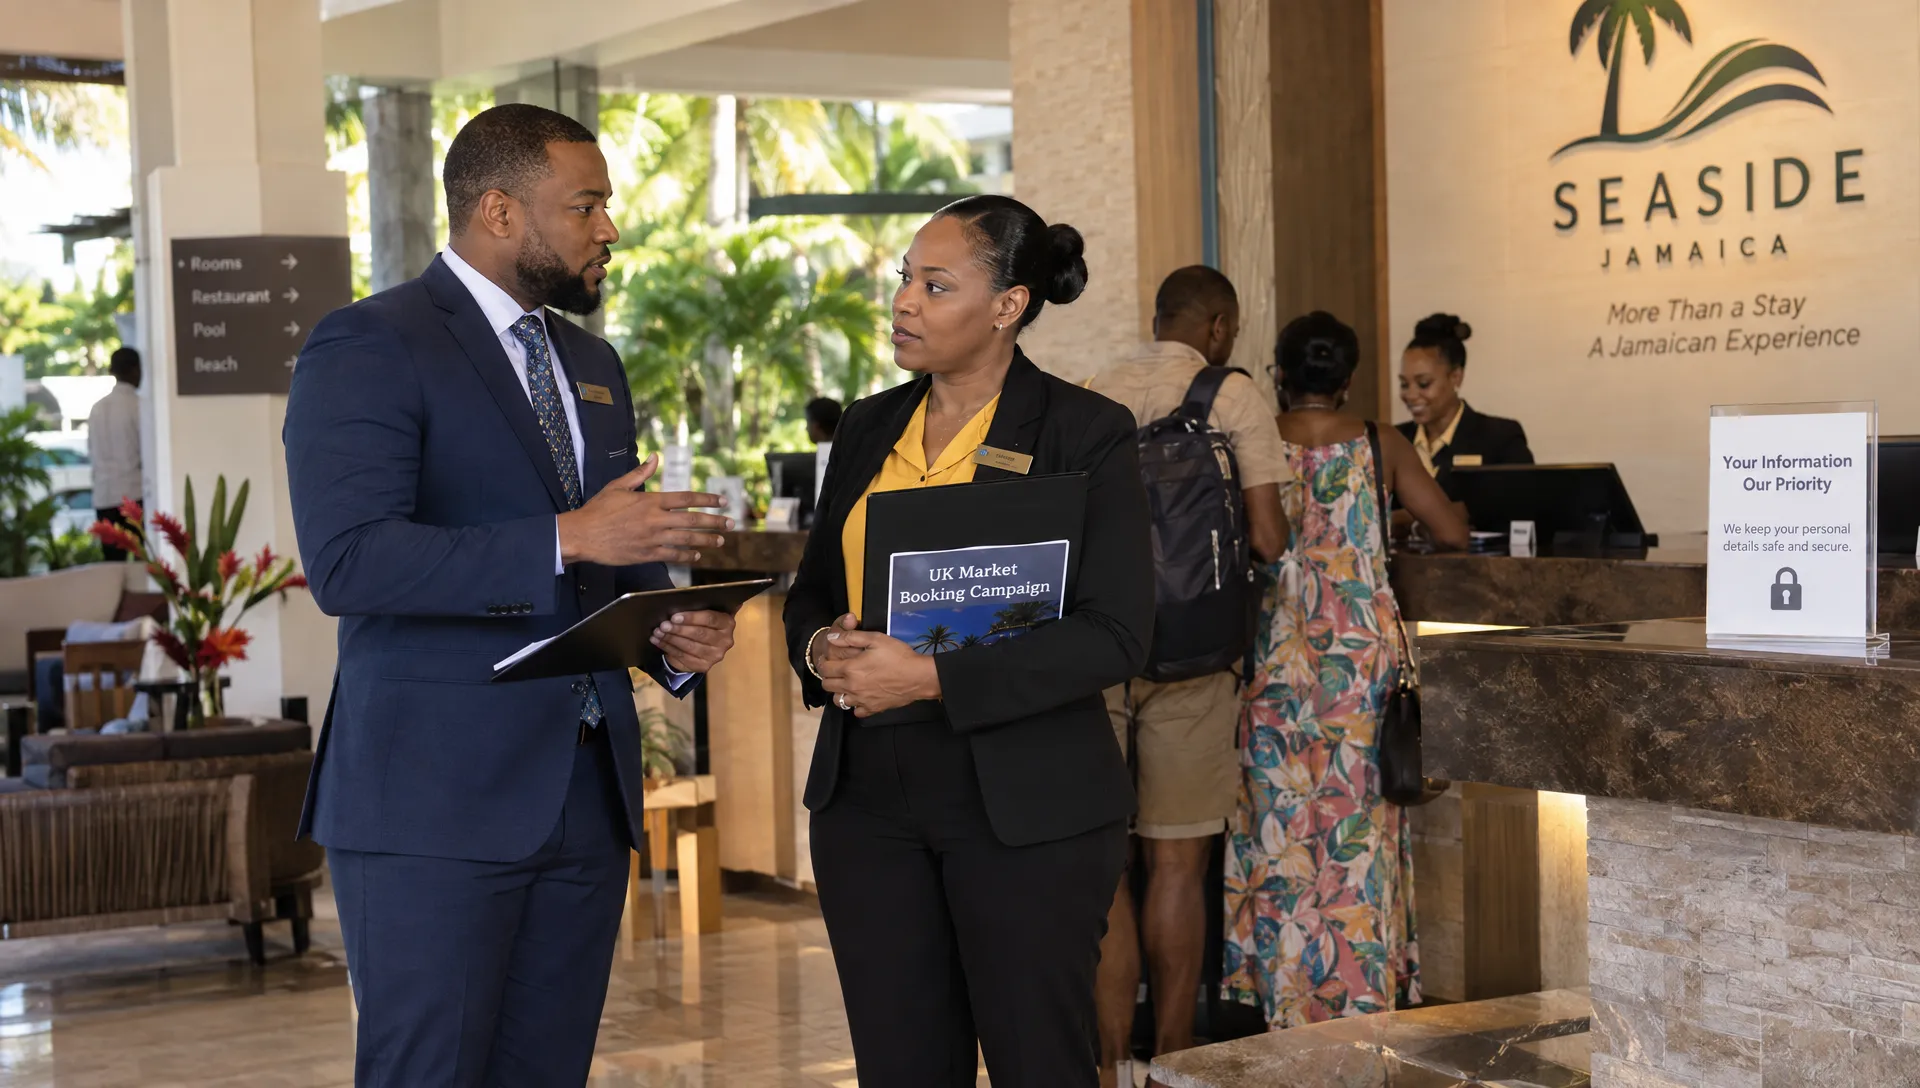
For example, a Jamaican resort running a campaign specifically to attract bookings from people in the UK should assess the associated enquiry and booking processing. The test concerns people who are in the UK in the relevant circumstances, not British citizenship alone.
Monitoring behaviour taking place in the UK
Tracking and analysing behaviour in the UK can also create a connection. Examples may include profiling people through an app or analysing identifiable location information about drivers operating there.
When assessing the Data Protection Act 2018 and UK GDPR, identify where the monitored behaviour occurs. Monitoring a British visitor's activities solely during a Jamaican holiday does not automatically satisfy the UK monitoring test merely because that visitor is British.
The presence of analytics software also requires a factual assessment. Consider what information is collected, whether individuals are tracked and how that information is subsequently used.
Providing services to a UK controller
A Jamaican processor does not automatically become directly subject to the UK GDPR merely because its customer is a UK controller. Its own establishment and activities still need assessment.
However, the UK controller will normally require a compliant processing contract. Instructions, confidentiality, security, subcontracting, assistance with rights requests and breach reporting can therefore become binding contractual duties for the Jamaican provider.
This distinction matters when negotiating liability: a contractual promise to meet UK standards is not the same as a legal conclusion that every part of the provider's business falls within UK jurisdiction.
What lawful processing requires
Where the UK regime applies, the Data Protection Act 2018 forms part of a wider compliance exercise, not a requirement simply to obtain consent from everyone.
The ordinary UK GDPR framework has seven principles: lawfulness, fairness and transparency; purpose limitation; data minimisation; accuracy; storage limitation; integrity and confidentiality; and accountability. In practical terms, a firm needs a justified purpose, an appropriate lawful basis, suitable safeguards and evidence that its decisions are defensible.
Consent is one possible basis, not the default. Depending on the activity and current statutory conditions, others include contractual necessity, legal obligation and legitimate interests. A contract basis requires genuine necessity for a contract with the individual, not merely a convenient connection to a business agreement. Ordinary legitimate interests require an assessment of purpose, necessity and the individual's interests and rights.
Health information and other special category data require an additional condition. Criminal offence data also has separate requirements. A customer contract alone does not resolve these issues, and applicable UK statutory conditions may require an appropriate policy document.
Handling access, correction and erasure requests
A Jamaican firm within the UK framework needs a reliable way to recognise requests, even when they arrive through customer service rather than a legal department. Individuals do not have to cite a statutory provision to exercise their rights.
For an access request, the organisation should identify the relevant processing, verify identity proportionately and search the systems reasonably required to respond. It should not demand a passport automatically where a less intrusive check would suffice.
The Data Protection Act 2018 also matters when considering exemptions, including those relevant to legal professional privilege. Exemptions require a proper assessment; ordinary commercial sensitivity is not a blanket reason to refuse access.
UK GDPR requests ordinarily require action within one month, subject to lawful extensions and applicable timing rules. Keep records of receipt, identity checks, searches, decisions and the response.
Correction and erasure need separate consideration. Inaccurate information may require rectification, but erasure is not absolute. Legal retention duties or the establishment, exercise or defence of legal claims can justify retaining particular records. Explain any refusal and the available complaint route.
Where a Jamaican provider acts only as a processor, it should normally refer the request to its controller and provide the assistance required by their agreement.
Separate territorial scope from international transfers
Whether UK law directly applies to a Jamaican business is different from whether a UK organisation can lawfully send personal data to it. A UK controller making information available to a separate Jamaican company, including through remote access, may be making a restricted international transfer.
The Data Protection Act 2018 does not replace the UK GDPR's transfer requirements. Establish which organisation initiates the transfer, who receives the information and whether UK adequacy regulations or another permitted route covers it.
Where appropriate, safeguards may include the UK International Data Transfer Agreement or the UK Addendum to the EU standard contractual clauses. EU clauses alone should not be assumed to satisfy UK requirements. Complete the assessment required by current UK transfer rules and address practical access risks, security and onward disclosures. The UK regulator's international transfer guidance is a useful implementation reference.
Consider a Jamaican cold-chain business that sources refrigerated-van conversions from a Dutch specialist while a UK logistics partner shares identifiable driver records with it. The vehicle supplier's location does not determine the rules governing those driver records. Each disclosure needs its own assessment of purpose, parties and transfer route.
A broader review of cross-border data handling can help distinguish UK transfers from separate EU and Jamaican requirements.

Assign responsibilities before problems arise
Governance, representatives and data protection officers
Once a business identifies an activity within scope, it should record whether it acts as controller, processor or, in some circumstances, joint controller. The label in a contract is relevant, but actual decision-making determines the role.
A non-UK business subject to the UK GDPR's targeting or monitoring provisions may need a UK representative unless an exemption applies. That appointment is different from appointing a data protection officer.
Under the framework containing the Data Protection Act 2018, DPO requirements turn on specified criteria, such as core activities involving large-scale regular and systematic monitoring or large-scale processing of certain sensitive information. A UK customer alone does not establish that a DPO is mandatory.
Useful implementation priorities include:
Map relevant activities: Record the individuals involved, their location, the information used and the UK connection.
Review agreements: Separate statutory duties from customer-imposed obligations and identify subcontractors.
Update notices: Explain purposes, lawful bases, recipients, retention and applicable rights accurately.
Test response procedures: Ensure staff can route rights requests and security incidents promptly.
Retain evidence: Keep the assessments, approvals and training records supporting compliance decisions.
Breach assessment and reporting
A personal data breach can involve accidental loss, alteration, destruction, unauthorised disclosure or unauthorised access. It is not limited to hacking: an email sent to the wrong recipient or a lost unencrypted device may qualify.
For processing governed by the UK GDPR, a controller must notify the UK supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware, unless the breach is unlikely to result in a risk to individuals' rights and freedoms. A likely high risk generally also requires communication to affected individuals without undue delay, subject to statutory exceptions.
The Data Protection Act 2018 does not make every security incident reportable. The organisation needs a documented assessment of whether personal data was compromised and the resulting risk. Even a decision not to notify should be recorded.
A processor must notify its controller without undue delay after becoming aware of a personal data breach. Customer contracts may require faster operational escalation. Do not assume that notifying a UK authority satisfies any separate Jamaican reporting obligation.
Regulators and enforcement are jurisdiction-specific
For UK matters, consult the UK supervisory authority's current guidance and reporting arrangements. UK reforms include changes to the regulator's statutory structure, making current official information preferable to assumptions based on older compliance materials.
Jamaica's Office of the Information Commissioner supervises the Jamaican framework. A Jamaican organisation may need to address local obligations alongside UK requirements, including applicable registration and governance duties.
Non-compliance can lead to investigations, corrective measures and financial penalties. Separately, a UK customer may pursue contractual remedies after a service failure. Compliance with the Data Protection Act 2018 therefore needs both a regulatory assessment and careful review of commercial commitments, rather than a generic promise to be “GDPR compliant”.
Frequently asked questions
Does having one UK customer automatically bring a Jamaican firm within UK law? No. Examine any UK establishment, whether the relevant processing relates to offering goods or services to people in the UK and whether it involves monitoring behaviour there. Contractual duties can still arise without direct application.
Does the Data Protection Act 2018 replace Jamaica's legislation? No. The UK Act and Jamaica's Data Protection Act, 2020 are separate laws. A business may have obligations under both, depending on its activities and circumstances.
How many data protection principles apply? Ordinary commercial processing under the UK GDPR is governed by seven core principles. The UK's Act also contains separate processing regimes, so the answer should not be generalised across every part of the legislation.
Do all Jamaican businesses need a UK representative or DPO? No. Each role has its own statutory criteria and exemptions. Neither appointment should be treated as a universal requirement for doing business with UK organisations.
Can a UK processing contract cover all international transfer requirements? Not necessarily. The processor terms and the lawful transfer mechanism address different requirements, even if they are documented together. Check both before access begins.
Review your firm's UK exposure
Start with a specific service, customer relationship or data flow rather than trying to classify the entire business at once. Identify the UK connection, establish each party's role and document which local, overseas and contractual requirements apply.
Henlin Gibson Henlin offers data privacy, compliance and risk legal services. A focused review can help your firm assess its UK-facing activities and align its agreements and procedures with the applicable requirements.
This article provides general information, not legal advice on a particular transaction or processing activity.